Resources
RFFR Provider Security Plan (PSP) Template
The Provider Security Plan (PSP) provides the Department with an overview of the applicable entity's operating environment, service delivery context, and security program supporting the delivery of Departmental services.
RFFR Provider Security Plan Annex (PSP-A) Template
The Provider Security Plan Annex (PSP-A) complements the Provider Security Plan (PSP) by describing the security controls implemented to support the secure delivery of those services and the protection of relevant information.
RFFR Security Assessment Questionnaire (SAQ) Template
The objective of the Security Assessment Questionnaire (SAQ) is to demonstrate to the Department that the applicable entity has implemented appropriate information security controls to support the secure delivery of Departmental programs.
External Systems Assurance Framework
This framework sets out the External Systems Assurance Framework (ESAF) under which the Department gains assurance over External IT Systems, and provides information for Providers.
Change of Circumstances Form
This form is to be completed by Service Providers and Third-Party Employment and Skills (TPES) system vendors to notify the Department of any change in circumstances that may alter the organisation’s risk profile.
DEWR ISMS Scheme
Outlines what the DEWR ISMS Scheme is, who it is for, and key considerations for all applicable stakeholders.
Third-Party IT Vendor Deed Guidelines
Provides Third-Party IT Vendor Deed Guidelines that form part of the Deed and provides information for Vendors on their continuing obligations.
ReadyTech's Esher House Cortex Accreditation Report
Refresh of the existing publication as a result of recent accreditation of TPES system Esher House
ReadyTech's JobReady Accreditation Report
Refresh of the existing publication as a result of recent accreditation of TPES system Job Ready.
ReadyTech's Ready Apprentice Accreditation Report
Refresh of the existing publication as a result of recent accreditation of TPES system Ready Apprentice
ReadyTech's Ready Recruit Accreditation Report
Refresh of the existing publication as a result of recent accreditation of TPES system Ready Recruit.
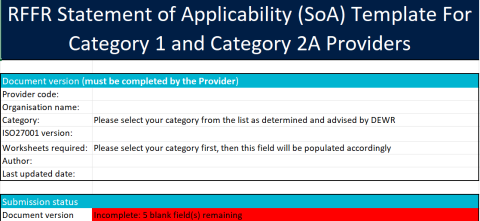
RFFR Statement of Applicability (SoA) Template
The Statement of Applicability (SoA) template includes controls from contractual obligations, Australian Government Information Security Manual (ISM) and ISO/IEC 27001 Annex A.
Right Fit For Risk (RFFR) Categorisation Questionnaire
The Categorisation Questionnaire helps the department understand how each Provider handles participant data and delivers services. This information is used to determine the Provider’s assurance category, which then sets the level of assurance they need to meet to achieve RFFR accreditation.
Right Fit For Risk (RFFR) ISO27001 Self-assessment report template
Provides example headings and guidance to be considered when Category 2A Providers are documenting their self-assessment.
Scope template
Provides example headings and guidance for documenting the ISMS Scope in accordance with ISO27001 clause 4, while also communicating key elements of the business, systems and information associated with delivering the Services and describing the provider’s implementation of the RFFR Core Expectation areas.
JobReady Live Accreditation letter
This is an accreditation letter to a third party employment system provider outlining their requirements and responsibilities for accreditation.
